Blog

Blog

Catch up on industry news, thought leadership, announcements, and more from Tanium.

Featured stories

Tanium Subscription Center

Get Tanium digests straight to your inbox, including the latest thought leadership, industry news and best practices for IT security and operations.

Subscribe now

Latest

Hunter Wins: HuntIQ Tradecraft is your new hunt library

The Hunt or be Hunted series tells the hunt stories. HuntIQ Tradecraft, now live on the Tanium Resource Center, gives you the playbooks to run them yourself.

Hunting Our Own Vulnerabilities First: Tanium’s Frontier AI Security Commitment

Tanium is using frontier AI models to hunt vulnerabilities in its own software before anyone else can. Here's what we're learning, and why customers should expect more security advisories and patches.

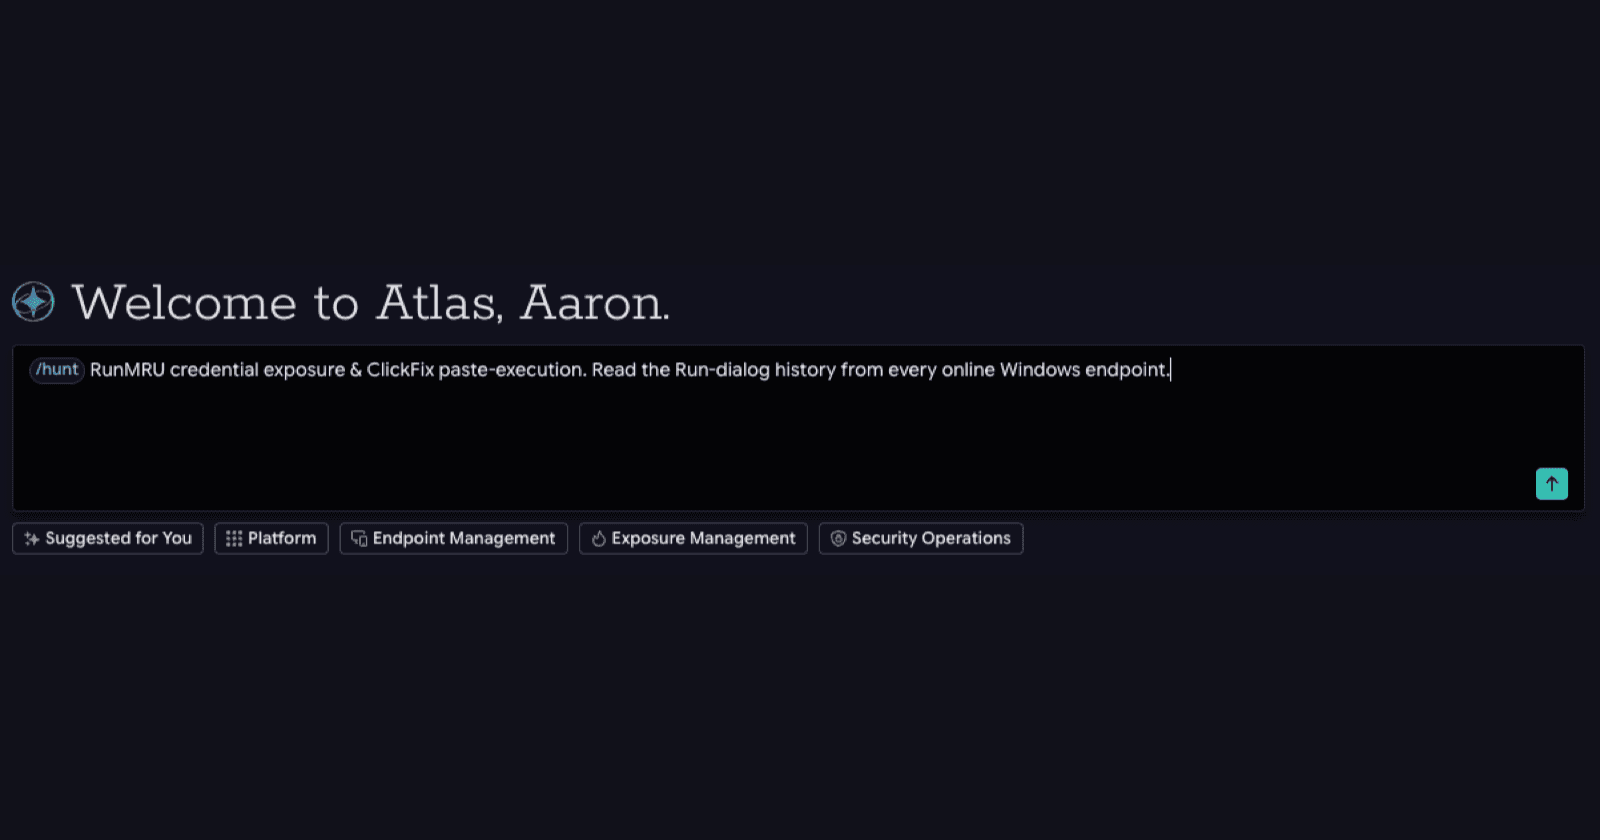
The Tanium Atlas prompt bar with a slash-hunt RunMRU credential-exposure command entered

A hunting playbook built for ClickFix went looking for pasted commands and found a working credential to a third-party portal instead.

The Tanium Atlas prompt bar with a slash-hunt FalconFlank command entered

Within 48 hours of the FalconFlank exploit's release, Tanium HuntIQ built seven behavioral detections and a single Atlas hunt prompt to catch attackers who turn CrowdStrike Falcon's own privileged clean-up against itself. See how Tanium Atlas sweeps an entire Windows fleet for the exposure in about a minute.

ShieldBreak Windows Defender zero-day

Learn how Tanium HuntIQ turned a Windows Defender zero-day into a tested mitigation before a CVE was assigned.

Analisi di mercato: un dito indica grafici finanziari su uno schermo touch

La BCE richiede alle banche sottoposte alla sua vigilanza diretta, i cosiddetti enti «significativi», un piano d'azione contro gli attacchi informatici basati sull'IA. In Italia, la Banca d'Italia ha esteso un'esigenza analoga a una larga parte del mercato che vigila direttamente a livello nazionale.

CVE-2026-65400: critical macOS Screen Sharing authentication bypass

CVE-2026-65400 is a pre-authentication vulnerability in the macOS Screen Sharing daemon (screensharingd) that lets a network attacker authenticate without valid credentials and gain root-level remote code execution. Apple patched the flaw on August 6, 2026, in macOS Tahoe 26.6.1, Sequoia 15.7.9, and Sonoma 14.8.9, but after reports of active exploitation, CISA rescored it from 7.1 to 9.8 (Critical) on August 14 and added it to the Known Exploited Vulnerabilities (KEV) catalog on August 18, giving federal agencies until August 21, 2026 to remediate.

Atlas chat showing the slash command picker with the hunt, investigate, and signal commands

With /hunt, /investigate, and /signal, Atlas turns a simple chat interaction into a guided SecOps workflow grounded in live endpoint state.

Line chart of total daily vulnerability findings from Tanium Exposure Management, holding near 20 billion from August 2025 through mid-June 2026 before spiking to roughly 100 billion by August 2026

Daily vulnerability findings across Tanium customer environments jumped from 10-40 billion to as high as 101 billion after mid-June 2026. Here is what is driving the surge and how to keep up.

Image of ShieldBreak Zero-day exploint

A public proof-of-concept called ShieldBreak fully bypasses Microsoft's patch for the Windows Defender privilege-escalation flaw known as RoguePlanet (CVE-2026-50656, CVSS 7.8), letting an attacker who already has local code execution reach a SYSTEM-level shell on Windows 11 25H2 and Windows Server 2025 with a reported 100% success rate. No Microsoft fix currently closes this bypass. Deploy the interim mitigation in the Guardian dashboard and hunt for the associated exploitation indicators until one ships.

Image of group of professionals looking at laptop screen
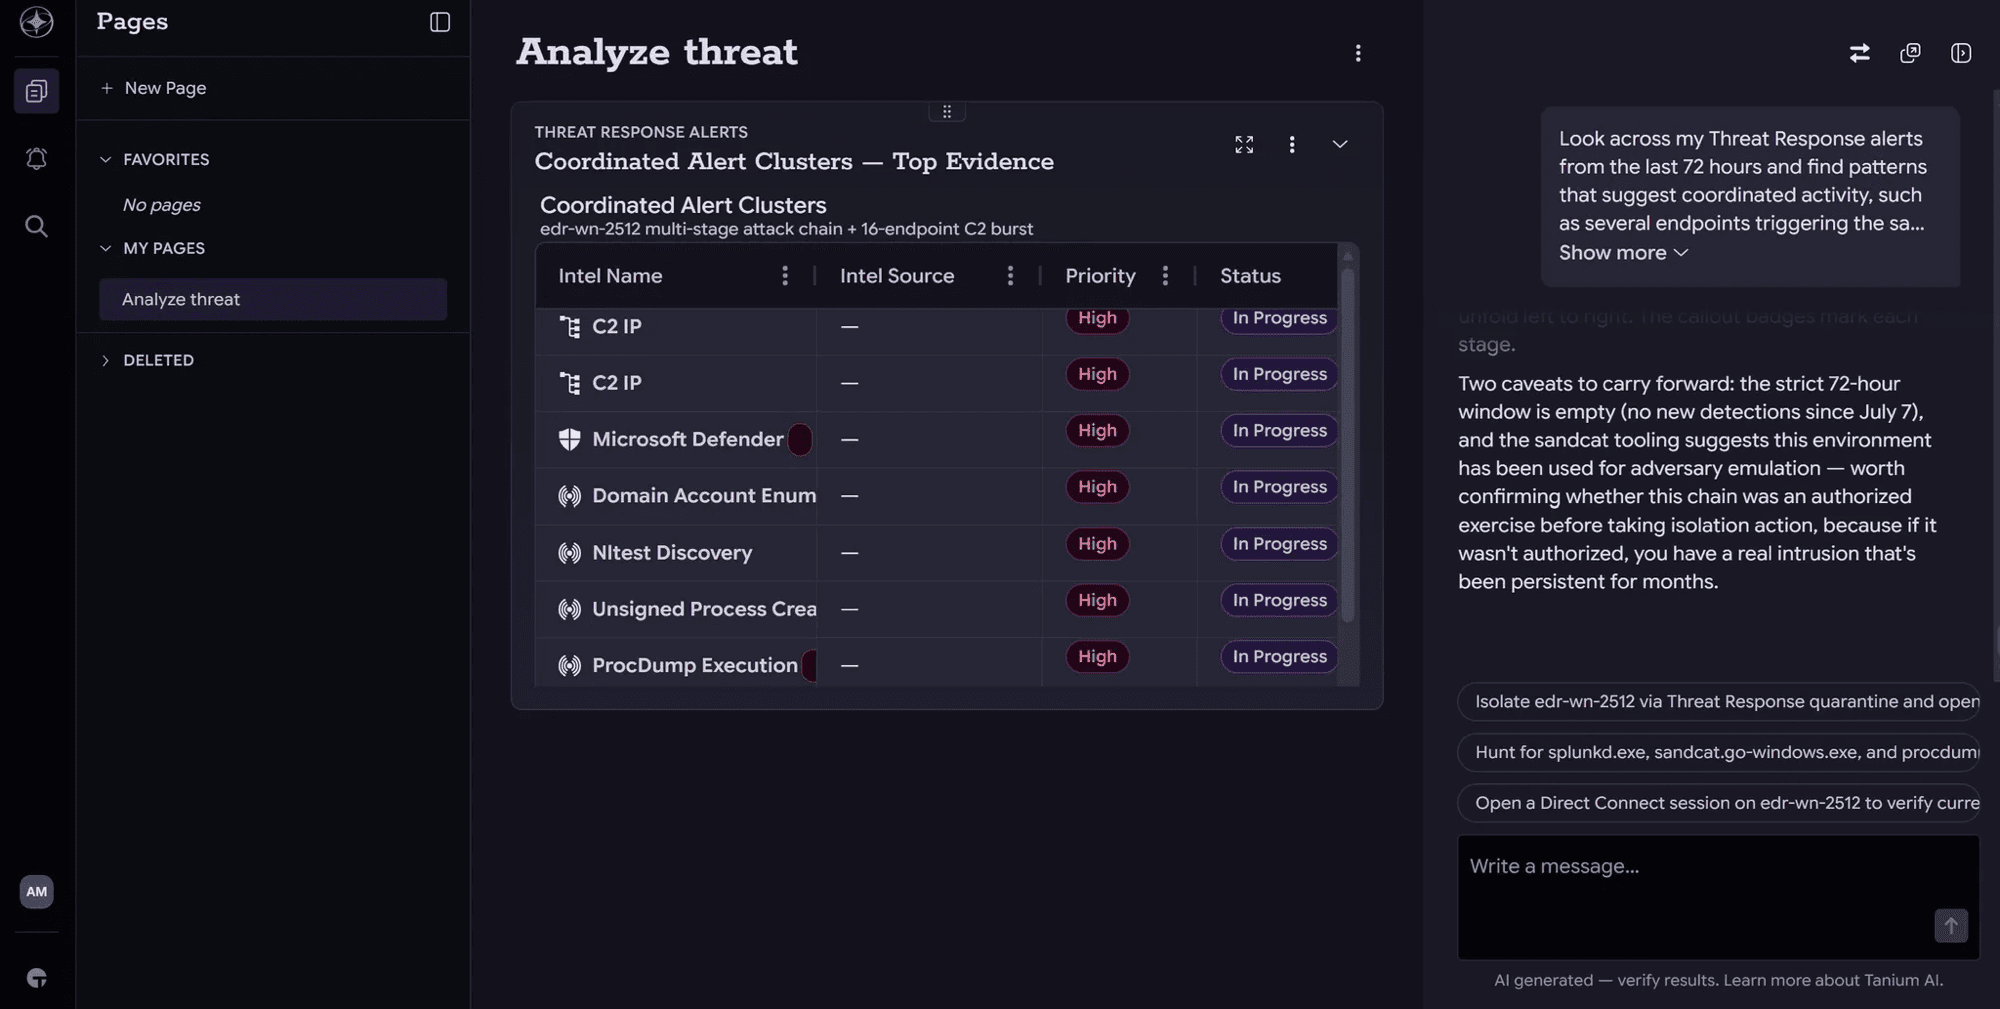
Agent-guided threat hunting in Tanium Atlas showing coordinated Threat Response alert clusters and AI-recommended next actions

Agentic SecOps changes the operating model: with Tanium Atlas, security teams can direct work in natural language, reason over live endpoint data, and keep humans in control.